
How tamper protects thousands of production hours for an innovative 3D animation studio.
Current Solutions, Challenges and Expected Outcomes:
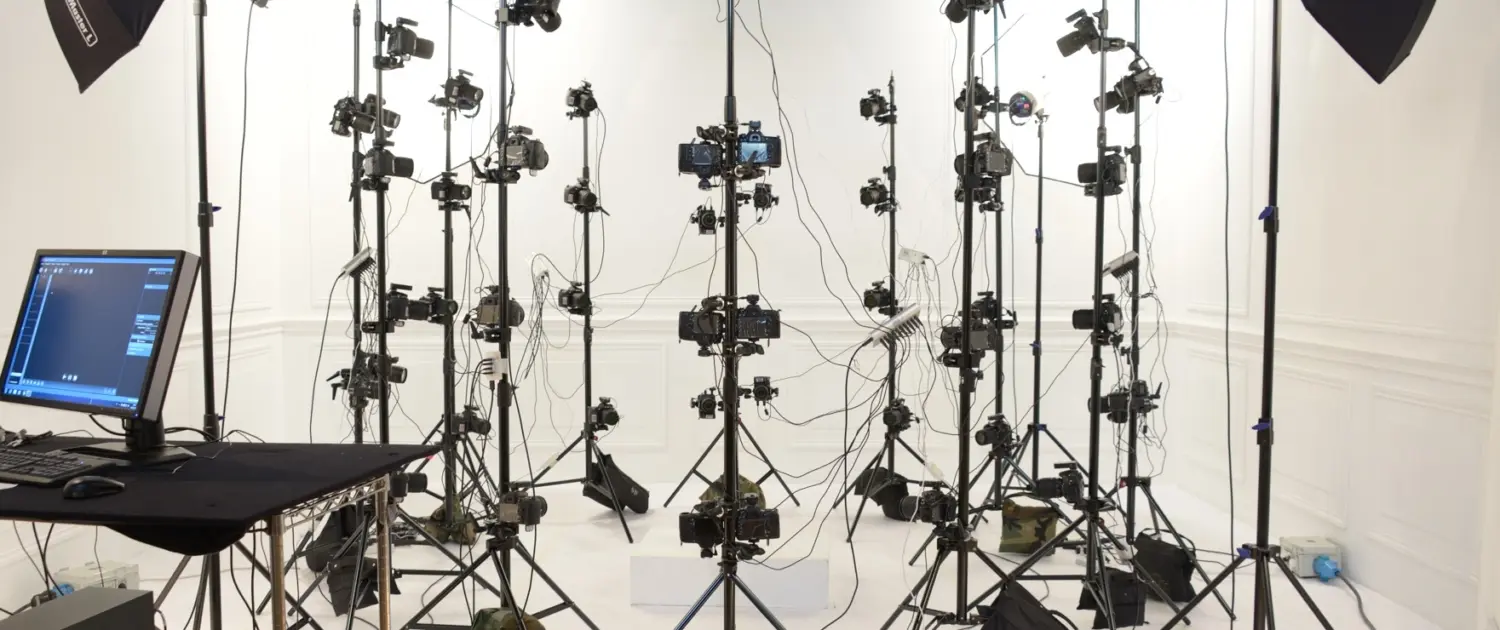
Our client, a creative industry company, is a 3D production studio based in the Paris region. It uses Backblaze B2 storage for its scalability and cost efficiency, hosting several hundred terabytes of raw footage, final renders, and 3D asset libraries accumulated over years of production, alongside copies retained on its on-premises file servers.
Seamless integration between Backblaze B2 and LucidLink facilitates real-time collaboration between distributed teams, while completed projects are archived to magnetic tape using StorageDNA to ensure their long-term preservation. Our client therefore has a robust storage and archiving infrastructure, but several aspects of its cybersecurity posture needed to be addressed.
The studio faces a major challenge: the commercial value of unreleased productions is enormous, and the leakage, corruption, or accidental deletion of an ongoing project could result in catastrophic financial losses.
Contractual confidentiality clauses with television broadcasters and producers impose strict requirements for access and modification traceability.
The main challenge was the lack of visibility into the integrity of large files, including multi-gigabyte 4K/8K renders, and the late detection of corruption, often discovered during the final stages of production.
Why tamper Was Chosen?
tamper was selected for its unique ability to monitor massive data volumes without affecting production workflows.
The AI-powered analysis of file modifications particularly appealed to the technical team. It makes it possible to immediately determine whether a multi-gigabyte render has been partially corrupted, altered by ransomware, or simply updated legitimately by the post-production team.
Native integration with Jira, already used for production tracking, enables the automatic creation of tickets whenever an anomaly is detected in critical assets.
Backblaze B2 bucket configuration scoring revealed previously overlooked weaknesses, including missing versioning on certain buckets and overly permissive settings, delivering immediate value even before the first audit.
Discover how tamper protects your critical data
Benefit from continuous integrity monitoring, proactive anomaly detection, and sovereign compliance across all your S3 buckets.
How tamper Operates Day to Day?
tamper performs daily audits across all the studio's Backblaze buckets, tracking every operation involving more than 15,000 files actively used in production.
Mass additions can signal the start of a new project or the ingestion of new raw footage, while deletions trigger tiered alerts based on the volume and criticality of the affected files.
In addition, integration with Grafana provides an extra layer of observability, correlating storage health metrics, such as latency and availability, with integrity events detected by tamper.
Why Do They Recommend tamper?
The studio recommends tamper as an essential safeguard against catastrophic incidents for any organization handling high-value assets.
FIM's ability to comprehensively track every operation provides legal protection during contractual negotiations. The studio can now formally demonstrate the integrity of its productions and provide evidence that they have not been disclosed before release.
The agentless approach eliminates latency and operational overhead, allowing creative teams to work without constraints while benefiting from continuous monitoring. In an industry where intellectual property is the primary asset, tamper transforms cloud storage into an auditable, traceable vault protected against modern threats.
The peace of mind provided by continuous visibility into production asset integrity has become a compelling selling point for demanding customers.
Explore other use cases
Discover how tamper secures strategic data for organizations with diverse requirements.